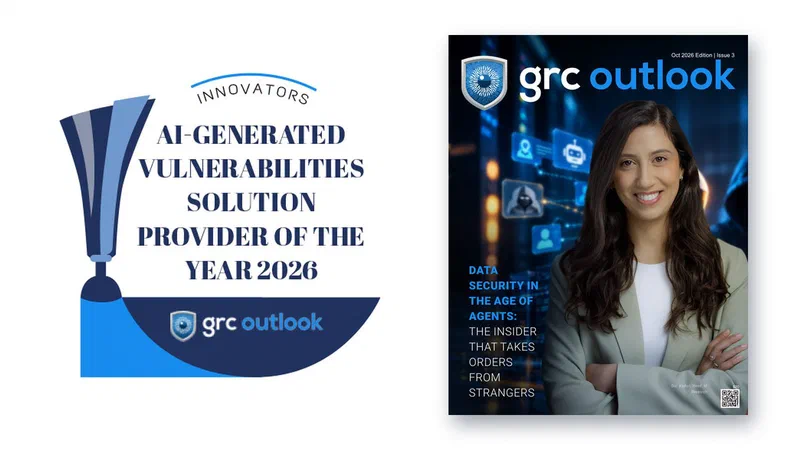
Waratek has been named the AI-Generated Vulnerabilities Solution Provider of the Year 2026 by GRC Outlook. The recognition is featured in the magazine’s October 2026 edition (Issue 3), where Waratek’s profile runs as a two-page spread on pages 18-19.
The profile, “Waratek: Securing the Autonomous Future of Application Security”, features Waratek Chair and CEO Doug Ennis and looks at how AI-assisted development has changed the security picture. Teams are generating code, and the patches for that code, faster than scanners and manual review can keep up with, while automated tools find and weaponize flaws in hours.
“As organizations rush to integrate artificial intelligence into their software pipelines, traditional security models simply cannot match the velocity of machine-generated code and all that comes with that. Our mission is to eliminate the false choice between rapid innovation and rigorous protection. By embedding security directly into the application runtime, we enable enterprises to move at maximum speed while maintaining complete, autonomous defense against both known and unseen threats.”
— Doug Ennis, Chair and CEO, Waratek
Runtime security from test to production
GRC Outlook highlights how Waratek covers both sides of the software lifecycle from inside the application runtime:
- Before release, Waratek IAST watches real execution paths and data flows during testing and reports only genuine, exploitable vulnerabilities, down to the exact file and line, so teams can fix AI-generated flaws in the build without triaging false positives.
- In production, Waratek RASP blocks exploits against known and zero-day vulnerabilities, whether the code was written by a person or an AI, and provides virtual patching with no source code changes, restarts or downtime.
“Relying on manual patch cycles or predictive scanners in an age of agentic AI attacks is no longer viable. Waratek shifts the focus by providing deterministic execution intelligence that stops exploits in their tracks without requiring code changes, development friction, or scheduled maintenance windows.”
— Doug Ennis
Read the full profile: Waratek on GRC Outlook, or see pages 18-19 of the October 2026 digital edition.
Want to see Waratek in action? Book a demo to see how IAST and RASP together protect your applications from AI-generated vulnerabilities.
About Waratek
Waratek offers Waratek IAST+RASP, the only compiler-based, runtime application tools that find vulnerabilities in the pre-production development pipeline, block attacks in production, and virtually patch flaws with no downtime or source code changes. Waratek IAST watches code execute to identify security flaws with absolute certainty, eliminating the “guesswork” and alert fatigue associated with traditional scanners. Waratek RASP intercepts and terminates unsafe operations at the JVM level, stopping attempts to change app behavior in attacks aimed at known and Zero Day vulnerabilities. Waratek is a trusted partner for organizations in global financial services, hospitality, healthcare, technology and other industries. Waratek has offices in Dublin, Ireland and Chicago, Illinois.